GR4VY

Credit card retries and routing logic: an updated guide
Every declined card costs more than the lost sale. It disrupts cash flow, frustrates customers, and raises support costs. Across global ecommerce, card decline rates can range from 5% to 20% depending on market and card type. Many of those declines are recoverable if merchants use the right retry and routing strategy.

Credit card retries and routing logic form the foundation of a modern payment stack. They decide when and where to send a transaction after an initial failure. They also determine which payment service provider (PSP) or acquirer should process each card to maximize approvals and control cost.

Merchants that rely on a single PSP often leave money on the table. A more advanced approach uses smart retry timing and dynamic routing to recover failed payments, reduce fees, and maintain global uptime.

What credit card retries are

A retry is an additional attempt to process a card after an initial decline. Declines happen for many reasons that are not permanent:

  • Temporary network failures
  • Issuer timeouts
  • Insufficient funds that resolve later in the day
  • Risk or fraud flags that can clear on a second try

Instead of losing the sale, merchants can attempt the charge again using predefined rules.

Types of retries

Simple retries: The same PSP resubmits the transaction after a delay. This approach is easy to set up but limited. If the PSP itself had a technical issue or if the card network flagged the transaction, repeating it on the same route often fails again.

Intelligent retries: The merchant applies logic about timing, amount, and routing. Examples include:

  • Waiting until a different time of day when bank systems are less busy.
  • Changing the amount if an authorization hold was partially approved.
  • Switching to another PSP if the first one failed.

Cascading retries: The transaction moves through a chain of PSPs or acquirers until one approves it. Each step uses different credentials or routing to improve success rates.

Why retries matter

Card declines cost more than lost revenue. They trigger support tickets, frustrate loyal customers, and cause subscription churn. Research shows that a well-planned retry strategy can recover 10–20% of failed payments in subscription businesses and reduce involuntary churn significantly.

Retries also help with cost control. Merchants can route retries through cheaper acquirers if the first attempt was declined for cost-related reasons such as cross-border interchange or network issues.

Finally, retries protect conversion in markets with complex banking systems. In Latin America, for example, local issuers sometimes reject global PSP traffic on the first attempt but approve later or through a local acquirer.

Common causes of card failures

Understanding decline reasons is the first step to planning retries.

  • Insufficient funds: Customers may have low balances early in the day but cover charges later.
  • Expired or replaced cards: Without updated details, recurring charges fail.
  • Issuer risk rules: Banks decline transactions that seem suspicious; a retry with clearer data can pass.
  • Incorrect authentication: PSD2 Strong Customer Authentication failures in Europe lead to soft declines. A second attempt after proper SCA can succeed.
  • Technical outages: PSP or network issues can cause temporary declines.

Merchants that collect decline codes and analyze patterns gain insight into how to time and route retries.

Basic retry strategies

Time-based retries

Retry after a set period, such as one hour or one day. This works for temporary issues like insufficient funds or network timeouts.

Dynamic timing

Adjust the retry interval based on decline reason or customer profile. For example, retry faster for network errors but wait a day for insufficient funds.

Amount adjustments

If the issuer allowed a partial hold, merchants can retry with the approved amount or split a payment into smaller charges.

Payment method update prompts

For recurring payments, trigger a card update request when retries fail due to expiration or replacement. Network tokenization also helps here by updating card data automatically.

Multiple route retries

Send the transaction to a different PSP or acquirer if the first attempt fails. This combines retry and routing logic for better results.

Why routing logic is the other half of the solution

Retries alone help, but routing decides where the payment goes in the first place. Merchants with more than one PSP can use rules to send each card to the path most likely to succeed.

Routing logic considers:

  • Card brand (Visa, Mastercard, Amex)
  • Card type (credit, debit, prepaid)
  • Issuer country
  • Currency
  • Historical approval rates by PSP

Static routing sends all transactions to one PSP per market. Dynamic routing evaluates each transaction in real time and chooses the best route.

Dynamic routing also enables cascading retries: if one PSP declines, the transaction moves to the next best route automatically.

Global impact of retries and routing

Worldwide merchants face different failure patterns:

  • In North America, interchange fees and fraud checks drive declines. Smart retries and routing to cost-efficient acquirers save money and improve approvals.
  • In Europe, PSD2 SCA failures cause many soft declines. Merchants need SCA-aware retries and routing that shifts to PSPs with better SCA handling.
  • In APAC, network errors and local issuer rules vary widely. Local PSPs often outperform global ones, making routing critical.
  • In Latin America, cross-border PSPs see higher declines than domestic acquirers. Retries through local routes often rescue sales.
  • In Middle East & Africa, mobile money and local card rails coexist. Merchants must route intelligently to match payment preferences.

For more on regional PSP and acquirer performance, see Card acquiring for international markets

Advanced routing models and real-time decisioning

Basic routing sends traffic to a single PSP per region. Advanced models evaluate each transaction in real time. They use performance data, card type, and regulatory factors to decide where to send a payment.

  • Real-time decision engines analyze approval rates, cost, and technical uptime.
  • Machine learning routing predicts which PSP will approve based on similar historical transactions.
  • Failover routing automatically moves traffic when one PSP times out or returns a soft decline.

This dynamic approach requires live data and strong integrations. Merchants that build it themselves face heavy development work. Those using orchestration platforms can configure rules and update them without code.

Static vs dynamic routing

FeatureStatic routingDynamic routing
PSP selectionFixed per market or card typeReal-time based on transaction attributes
Response to outagesManual switchAutomatic failover
Approval optimizationLowHigh, uses historical performance and cost data
Implementation effortLower upfront, harder to scaleHigher setup but easier to adapt long term
Global scalabilityLimitedDesigned for multi-market, multi-PSP

Dynamic routing is a key upgrade for merchants aiming to reduce decline rates worldwide.

Advanced retry strategies

Retries become more powerful when combined with dynamic routing:

  • Smart intervals: Instead of retrying every decline at the same time, adapt intervals to issuer behavior. For example, retry insufficient funds after a full day but retry network errors within minutes.
  • PSP cascading: Send a failed transaction to another PSP rather than retrying with the same one.
  • Card type rules: Some acquirers perform better with debit vs credit or prepaid. Merchants can retry by switching PSP based on card type.
  • Amount adjustments: Break a high-value charge into smaller retries if the first attempt failed due to issuer risk filters.

Retries must respect card network rules. Excessive retries can look like fraud and trigger higher decline rates.

Compliance considerations

Retries and routing must fit within the rules set by regulators and card networks.

PSD2 and SCA

In Europe, PSD2 requires Strong Customer Authentication for most transactions. If a transaction fails due to SCA, a retry must trigger proper authentication or apply a valid exemption.

PCI DSS

Owning card data to power retries and routing requires compliance with PCI DSS standards. Merchants must secure data storage and tokenization.

Data localization

Some countries require payment data to remain within their borders. Merchants must choose PSPs and vaults that comply.

Card network rules

Visa and Mastercard monitor retry behavior. Merchants should avoid repeated identical attempts that look like fraud.

For a deeper look at compliance frameworks in complex payment setups, see Why payment orchestration matters for European merchants expanding cross-border.

Regional adaptation of retries and routing

Different markets require different strategies:

  • North America: Interchange costs matter. Route retries to acquirers with better cost structures and strong risk tools.
  • Europe: PSD2 SCA soft declines require retry flows that re-trigger authentication or use exemptions.
  • APAC: Local PSPs often outperform globals, especially with domestic card schemes. Routing to them first raises approval.
  • Latin America: Retry cross-border declines through local acquirers. Approval lifts are often double-digit.
  • Middle East & Africa: Combine card routing with local methods like mobile wallets. Retries should consider alternative rails where card acceptance is low.

These patterns highlight the need for flexible architecture. Merchants tied to a single PSP cannot adapt quickly.

How orchestration simplifies retries and routing

Managing retries and routing across multiple PSPs is difficult without a unifying layer. Payment orchestration solves this by bringing control, compliance, and flexibility into one platform.

One integration for many PSPs

Merchants integrate once with an orchestration platform. Adding a new PSP or acquirer no longer requires building and testing new code. This keeps development teams focused on product rather than maintaining payment pipes.

Centralized compliance and security

Handling card data across multiple providers triggers PCI DSS responsibilities. Orchestration platforms provide a single secure vault, reducing exposure and making compliance audits easier. They also help meet regional requirements such as data localization laws in Europe, Brazil, and parts of Asia.

Dynamic routing without custom development

Orchestration engines make it possible to create complex routing rules through a dashboard. Merchants can route by card type, issuer country, or cost without writing custom code. They can also create failover paths to protect against outages automatically.

Unified fraud and risk tools

When PSPs use different fraud filters, gaps appear. Orchestration platforms let merchants apply one fraud policy across all routes. This keeps protection consistent and reduces unnecessary declines.

Reporting and reconciliation in one place

Finance teams no longer have to pull reports from several PSP dashboards. Orchestration combines settlement data, dispute records, and authorization metrics into a single view.

For a deeper comparison, see Payment orchestration vs PSP in Europe and Top 10 benefits of using payment orchestration in 2025.

Strategic roadmap for global merchants

Building a high-performance retry and routing system is a staged process. Merchants can follow this roadmap:

1. Audit current PSP performance

Track approval rates, downtime, and processing fees. Identify regions or card types with weak results.

2. Map decline reasons

Analyze issuer response codes. Separate soft declines (recoverable) from hard declines (permanent). This drives retry timing and routing rules.

3. Select pilot markets

Choose one or two regions with clear performance or cost gaps. Avoid launching worldwide at once.

4. Deploy orchestration

Integrate an orchestration platform to handle routing, retries, and fraud. This avoids building custom infrastructure.

5. Configure smart routing

Set rules by brand, BIN, or cost. Add failover PSPs. Monitor approval rate changes.

6. Implement intelligent retries

Schedule retries based on decline reason and region. Use PSP cascading for better recovery.

7. Benchmark and renegotiate

Use performance data to negotiate better rates with PSPs. Merchants with volume spread across providers gain leverage.

8. Scale globally

Once the model works in pilot markets, expand to new countries. Add local PSPs or acquirers where they outperform global ones.

9. Maintain continuous optimization

Payments are not static. Routinely review data, update rules, and adjust PSP mix to maintain cost and approval efficiency.

FAQ

What is the difference between retries and routing logic?

Retries are additional attempts after a decline. Routing logic decides where a payment goes initially and where it should be retried for better success.

Do retries violate card network rules?

No, if done correctly. Excessive identical retries can look like fraud. Merchants should space retries and follow network guidance.

Does dynamic routing always improve approvals?

It usually does, but results depend on the quality of data and the PSP mix. Merchants must track performance and adjust rules.

Is PCI DSS compliance harder with multi-PSP setups?

Yes, unless using orchestration. A central vault keeps card data secure and reduces scope.

Can orchestration work with both global and local PSPs?

Yes. Orchestration is designed to connect global providers and regional specialists through one integration.

What role does SCA play in retries?

If a transaction fails due to PSD2 SCA, the retry must trigger correct authentication or apply a valid exemption to succeed.

Card declines are not always final. Merchants that use credit card retries and routing logic can recover lost revenue, reduce fees, and improve global performance. The challenge is complexity: building and maintaining multiple PSP connections, applying smart retry timing, and staying compliant across regions.

Payment orchestration turns this challenge into a manageable strategy. It centralizes data, automates routing, and applies consistent fraud and compliance controls. Merchants gain the flexibility to add PSPs, reroute in real time, and negotiate better rates.

Contact Gr4vy to simplify retries and routing logic, reduce failed payments, and build a payment stack ready for global growth.
Multi-PSP credit card processing: global strategies for merchants

Merchants who operate across countries face constant pressure on payments. Customers expect cards to work every time, regulators demand compliance, and acquirers vary widely in performance. Relying on a single PSP leaves businesses exposed to outages, high fees, and approval gaps.

A multi-PSP strategy spreads that risk. By connecting to several payment service providers, merchants improve resilience, expand reach, and protect revenue. The challenge is managing the complexity that comes with it. This article explores what multi-PSP credit card processing means, why global merchants are adopting it, the challenges they face, and how orchestration solves the gaps.

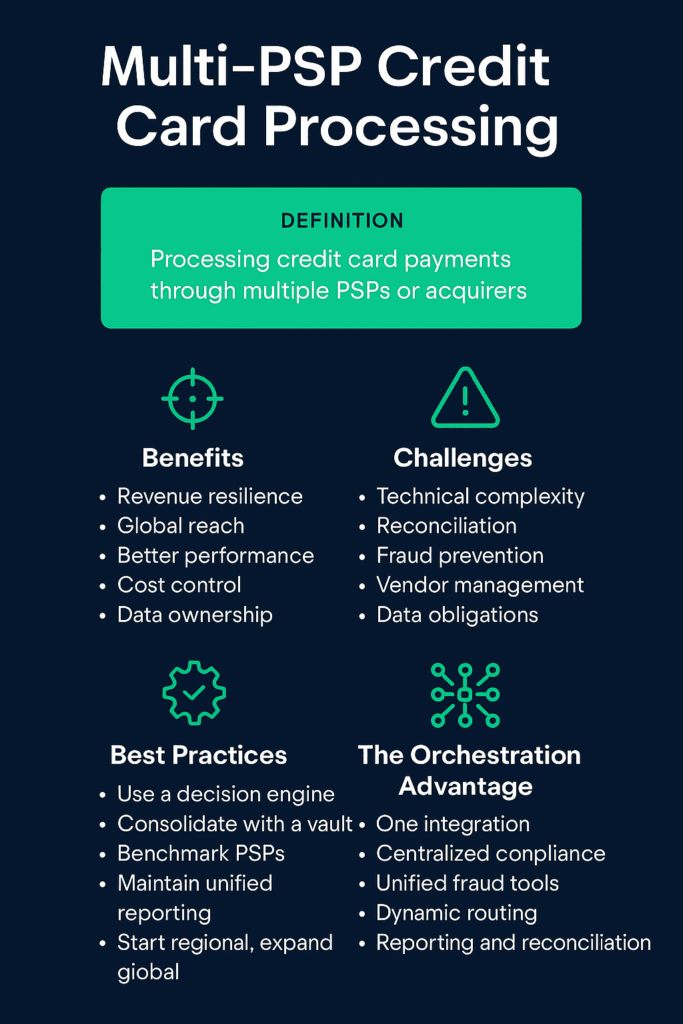
What is multi-PSP credit card processing?

Multi-PSP processing is the practice of working with more than one payment service provider to handle card transactions. Instead of sending every transaction through one PSP, merchants use routing logic to decide where each payment goes.

The setup usually includes:

  • Routing engine: rules that direct payments to the right PSP.
  • Fallback path: if one PSP goes down, traffic shifts to another.
  • Data control: owning the card vault so data is not locked into one provider.
  • Reconciliation tools: dashboards and reports that combine data from several PSPs.

This approach is different from relying on one PSP that controls the entire process. With a single PSP, merchants have less flexibility and less control over costs and approval rates. For a deeper look at how card schemes and acquirers connect, see How does a credit card scheme work?.

Why merchants adopt multi-PSP strategies

Higher resilience

A single PSP outage can stop payments in one or more markets. Multi-PSP setups allow merchants to route payments elsewhere and avoid downtime. This protects revenue and customer trust.

Global reach

No PSP is strong everywhere. Local acquirers often perform better than global ones in certain markets. Working with multiple PSPs ensures merchants can meet regional scheme requirements and customer preferences.

Better approval rates

Routing to the provider with the highest approval rates for a card type or region reduces declines. This is one of the main reasons merchants see revenue lift when adopting a multi-PSP model.

Cost optimization

Competition between PSPs gives merchants leverage. By comparing fees and routing volume strategically, they reduce processing costs.

Data ownership

Owning the card vault keeps merchants independent. They are not locked into one PSP’s token system and can move traffic freely. For more context, see Top 10 benefits of using payment orchestration in 2025.

Challenges of a multi-PSP approach

Technical complexity: Integrating and maintaining multiple PSPs requires development time and constant updates. Each PSP has its own API structure and operational quirks.

Reconciliation issues: Reporting across providers can be messy. Settlement timing, formats, and fee structures differ, making it difficult to build a clear financial picture.

Fraud management: When PSPs apply fraud tools differently, gaps appear. Merchants must create a unified fraud strategy that sits above the PSP layer.

Vendor management: Working with multiple PSPs increases contract complexity. Merchants must manage separate service levels, pricing agreements, and compliance obligations.

Data security and compliance: Handling card data across multiple providers heightens PCI DSS responsibilities. Merchants must also consider regional data localization rules.

Global and regional considerations

Multi-PSP adoption looks different across regions.

North America

The US and Canada remain card-heavy, with high interchange fees and growing fraud challenges. Multi-PSP setups give merchants flexibility to work with local acquirers or specialized providers that handle high-risk segments.

Europe

Regulation drives much of the strategy. PSD2 and Strong Customer Authentication add layers of compliance. Local schemes like Girocard in Germany or iDEAL in the Netherlands make regional PSPs valuable.

APAC

This is one of the most fragmented markets. Super-app wallets dominate in some countries, while credit card penetration remains high in others. Merchants need local PSPs to reach customers effectively.

Latin America

Approval rates are often stronger with local acquirers than with global PSPs. Installment payments and regional methods add complexity. A multi-PSP model is often essential for conversion.

Middle East & Africa

Card penetration is growing, but regulation and banking structures vary widely. Mobile money and local rails are often more trusted than cards. Merchants that combine PSPs gain access to these regional methods.

For more insight on regional strategies, see Card acquiring for international markets.

Best practices for multi-PSP credit card processing

Adopting a multi-PSP model is not only about connecting to more providers. Merchants must design the system so it improves performance without overwhelming teams. The following practices have proven effective:

Use a decision engine for routing

Transactions should not be distributed randomly. A decision engine applies rules based on card type, geography, and historical performance. For example, a merchant might send Visa transactions in Brazil to a local PSP with higher approval rates, while routing Mastercard transactions to a global PSP with lower fees.

Consolidate card data in a secure vault

Owning the vault means card data remains portable. Merchants who depend on a PSP’s vault find it hard to switch. A unified vault ensures that tokens work across PSPs, reducing lock-in and enabling smooth migration.

Benchmark PSP performance regularly

Authorization rates change over time. Merchants should run A/B tests across providers to find the best-performing route. Benchmarks also give leverage in negotiations, showing PSPs they must stay competitive.

Maintain unified reporting dashboards

Having five different PSP portals is not sustainable. Consolidated dashboards give finance teams one view of revenue, fees, and disputes. This is essential for reconciliation and compliance audits.

Start regional, expand global

Rolling out multi-PSP globally in one step adds too much risk. The better path is to pilot in one region, refine routing rules, then expand. This phased approach helps merchants manage complexity while scaling.

For merchants balancing multiple regions and payment types, see How to accept alternative payment methods for broader strategies.

multi psp credit card processing

The orchestration advantage

Without orchestration, multi-PSP setups are difficult to manage. Orchestration platforms solve these challenges by creating one control layer between merchants and PSPs.

One integration for many PSPs: Instead of building and maintaining multiple APIs, merchants integrate once with the orchestration platform. Adding a new PSP becomes a configuration task instead of a full development project.

Centralized compliance: PCI DSS, PSD2, and data localization are major concerns when handling card data across borders. Orchestration provides a single vault, reducing exposure and ensuring compliance frameworks are applied consistently.

Unified fraud tools: Fraud prevention can sit above the PSP layer, applying the same rules to every transaction. This prevents gaps caused by PSPs using different tools or standards.

Dynamic routing and failover: Orchestration engines route payments in real time, using rules based on approval rates, cost, or risk. If one PSP fails, the system automatically retries with another, keeping the checkout experience smooth.

Reporting and reconciliation: Orchestration collects transaction data from every PSP and presents it in one interface. Finance teams gain visibility across providers, making it easier to reconcile fees and settlements.

For more, see Payment orchestration vs PSP in Europe and Why payment orchestration matters for European merchants expanding cross-border. While both articles emphasize Europe, the orchestration value applies worldwide.

Strategic roadmap for global merchants

Building a multi-PSP strategy requires planning. The following roadmap helps merchants approach it step by step:

  1. Audit current PSP performance: Measure downtime, authorization rates, and costs. This baseline reveals where a second PSP might add the most value.
  2. Select a test market: Choose one region where performance or costs are a problem. Use this as the pilot for multi-PSP integration.
  3. Implement orchestration: Connect PSPs through an orchestration layer to simplify routing, fraud prevention, and reconciliation.
  4. Benchmark and refine: Run comparisons between PSPs. Adjust routing rules to maximize approval rates and minimize fees.
  5. Expand globally: Once the pilot is successful, scale to other regions. Use local PSPs where they outperform global providers.
  6. Leverage negotiation: Use performance data to negotiate better terms with PSPs. Merchants with multi-PSP setups have more bargaining power.
  7. Maintain continuous monitoring: PSP performance changes over time. Regular monitoring ensures the routing strategy stays optimal.

This roadmap helps merchants move from single PSP reliance to a resilient, data-driven multi-PSP system.

FAQ

What is the difference between a PSP and an acquirer?

A PSP provides the technology layer to connect merchants with acquirers. An acquirer is the financial institution that processes the card transaction. Merchants often use PSPs to access multiple acquirers.

Does multi-PSP processing always reduce costs?

Not always. Savings depend on routing strategy and negotiation. Costs can increase if the setup is not managed well. Orchestration helps optimize for both fees and approval rates.

How does reconciliation work across PSPs?

Each PSP settles funds differently, creating reporting challenges. Orchestration platforms unify settlement data, making reconciliation easier.

Does fraud risk increase with multiple PSPs?

If managed poorly, yes. But orchestration allows merchants to apply consistent fraud rules across all providers, reducing overall risk.

Can orchestration integrate both global and local PSPs?

Yes. Orchestration is designed to connect global players and local champions, giving merchants the best of both worlds.

Multi-PSP credit card processing is no longer a luxury for global merchants. It is a strategy that protects revenue, improves performance, and creates leverage with providers. The challenge lies in managing the complexity, which is where orchestration proves essential.

Merchants that adopt orchestration gain control over routing, compliance, and fraud prevention. They build resilience into their payment stack and keep pace with customer expectations in every market.

Contact Gr4vy to simplify multi-PSP credit card processing and scale payments worldwide.

How European merchants can reduce chargebacks and protect revenue in 2026

Chargebacks remain one of the most persistent risks in European ecommerce. Every dispute costs more than the transaction itself, eating into margins through lost revenue, fees, and operational strain. For merchants, the real risk is not only the financial loss but also the reputational impact and the potential for penalties if chargeback ratios rise too high.

In 2026, European chargeback dynamics are being reshaped by regulation, consumer protection, and new payment methods. Merchants need to understand the rules, identify the risks, and apply practical strategies to minimize disputes. This article explores the key drivers of chargebacks in Europe, the rules that govern them, and how merchants can protect their revenue.

Understanding chargebacks in Europe

A chargeback occurs when a cardholder disputes a transaction with their bank or card issuer. The bank reverses the payment, and the merchant must either provide compelling evidence to contest it or absorb the loss.

Chargebacks differ from refunds in two ways:

  • Refunds are initiated by the merchant as part of customer service.
  • Chargebacks are initiated by the issuing bank after a dispute.

Card scheme rules

Visa, Mastercard, and American Express each define their own chargeback codes and timelines. These rules apply across Europe, but implementation may differ depending on local acquiring banks. Merchants that operate across borders must stay aware of multiple sets of requirements.

PSD2’s role

The revised Payment Services Directive introduced Strong Customer Authentication (SCA), designed to reduce fraud-related disputes. While SCA helps prevent unauthorized transactions, it has not eliminated chargebacks. Merchants must still prove compliance with SCA exemptions during disputes.

Chargeback rates in Europe

On average, ecommerce chargeback rates in Europe remain below 1%, but certain verticals (such as travel, digital goods, and marketplaces) regularly exceed this threshold. Card networks monitor ratios closely, and merchants that cross tolerance levels face fines or higher processing fees.

Data from 50 payment and merchant statistics shaping Europe in 2025 shows that fraud-related disputes now account for a growing share of chargebacks, underscoring the need for better prevention tools.

Key risks driving chargebacks

Fraudulent transactions

Fraud remains the most common driver. Two categories dominate:

  • Friendly fraud: When a customer makes a legitimate purchase but later disputes it, often claiming they did not authorize the transaction.
  • Account takeover: When stolen credentials are used to complete transactions without the customer’s consent.

Customer dissatisfaction

Disputes also arise when customers claim goods were not delivered, arrived damaged, or did not match descriptions. Poor communication or unclear refund policies often push customers toward banks instead of merchants.

Processing errors

Duplicate charges, incorrect transaction amounts, and settlement mistakes also lead to disputes. Even small operational errors create costly chargebacks.

Regional differences

Chargeback risks vary by payment method and country:

  • SEPA Direct Debit: Customers can request a refund within eight weeks of a debit. This makes disputes easier for consumers and riskier for merchants.
  • Wallets and APMs: Dispute rules differ widely, often offering buyers more protection than traditional card rails.

For a closer look at these payment preferences, see our guide on top payment methods in Europe.

European chargeback rules and compliance requirements

Merchants face overlapping rules when it comes to chargebacks.

PSD2 and SCA compliance

Merchants must prove they followed SCA requirements or that an exemption applied. If they cannot, issuers often side with the cardholder.

SEPA Direct Debit refund rights

In the eurozone, SEPA gives customers the right to request a no-questions-asked refund within eight weeks. Beyond that, unauthorized debits can be disputed for up to 13 months.

GDPR considerations

Dispute resolution requires handling sensitive personal and financial data. Merchants must ensure compliance with GDPR when collecting, processing, and submitting evidence.

Country-level enforcement

While card scheme rules are global, European regulators and local courts play a role in disputes. For example, Germany’s consumer protection agencies may pressure merchants with high complaint volumes, while the UK’s Financial Ombudsman can intervene in disputes.

For a deeper dive into how European compliance overlaps with payments, see our guide on embedded payments compliance in Europe.

Strategies to reduce chargebacks

Merchants can lower dispute rates and protect revenue with practical measures tailored to Europe’s regulatory and consumer environment:

  1. Strengthen authentication: Apply SCA correctly on initial transactions and use exemptions responsibly for recurring or low-value payments. This ensures compliance and reduces fraud-driven disputes.
  2. Set clear refund and cancellation policies: Transparent policies reduce the chance that customers go directly to their bank. Easy-to-access refund options also improve trust.
  3. Use proactive communication: Send real-time notifications on billing dates, shipping updates, and renewals. Customers who feel informed are less likely to file chargebacks.
  4. Adopt tokenization and secure storage: Tokenization protects card data and minimizes risk of misuse. It also supports account updater services that reduce disputes linked to expired cards.
  5. Automate alerts and monitoring: Early alerts from card networks allow merchants to resolve issues before they escalate into formal chargebacks.

For more insights into how regional habits shape dispute trends, see our report on digital wallets in Europe.

Also, you can access here an industry benchmark covering fraud, payments and dispute trends.

How orchestration helps manage chargebacks

Chargebacks become harder to manage when merchants rely on multiple acquirers or PSPs. Payment orchestration provides the tools to bring dispute management under one roof:

  • Centralized reporting: Collect dispute and chargeback data from all providers in one dashboard.
  • Routing flexibility: Direct high-risk transactions through acquirers with stronger fraud defenses or better win rates in disputes.
  • Unified evidence management: Orchestration platforms consolidate transaction records, making it easier to submit compelling evidence.
  • Third-party fraud tools: Easy integration of external fraud detection services strengthens prevention.

This orchestration advantage mirrors the broader benefits outlined in our guide on payment orchestration vs PSP in Europe.

Roadmap for merchants

To prepare for 2026, European merchants should:

  1. Map chargeback exposure: Understand which markets, methods, and products drive the most disputes.
  2. Train staff: Ensure customer service and risk teams understand local chargeback rules and evidence requirements.
  3. Integrate orchestration: Adopt orchestration to centralize fraud prevention, evidence gathering, and dispute resolution.
  4. Balance risk and conversion: Stronger controls reduce fraud but can impact approval rates. Use orchestration to fine-tune the balance.
  5. Review compliance regularly: Regulations like PSD3 will continue to evolve. Merchants must adapt quickly to stay compliant.

More context on regulatory shifts and consumer expectations is available in our report on European retail payment trends in 2025.

FAQ

What causes most chargebacks in Europe?

Fraudulent transactions, friendly fraud, and customer dissatisfaction remain the top causes.

Are chargeback rules the same across all EU countries?

No. While card scheme rules are consistent, local enforcement and refund rights, especially with SEPA Direct Debit, vary by country.

How does PSD2 affect chargebacks?

PSD2 introduced Strong Customer Authentication, which reduces unauthorized fraud. But merchants must apply exemptions correctly or risk declines and disputes.

Can merchants fight chargebacks successfully?

Yes, but success depends on having clear evidence, centralized reporting, and strong internal processes.

Does orchestration help reduce chargeback costs?

Yes. Orchestration centralizes data, simplifies dispute handling, and improves routing strategies that reduce dispute frequency.

Chargebacks are costly, but European merchants can reduce their impact by strengthening compliance, improving communication, and using technology to manage disputes more effectively.

Orchestration provides the structure to prevent, manage, and resolve chargebacks across multiple markets and providers. It reduces operational complexity while protecting revenue.

Contact Gr4vy to simplify chargeback management and protect your business in 2026.

What are the most popular alternative payment methods in Europe?

Alternative payment methods (APMs) are no longer optional in European ecommerce. Consumers across the region increasingly choose wallets, bank transfers, and local payment schemes over traditional cards. For merchants, ignoring these methods means lost revenue and lower conversion rates.

APMs are also closely tied to compliance. PSD2, GDPR, and national rules govern authentication, data handling, and customer rights. Merchants expanding across Europe must integrate APMs in ways that respect both consumer preferences and regulatory requirements.

This article explains the growth of APMs in Europe, outlines country-level adoption, and highlights how orchestration simplifies integration across diverse markets.

Growth of alternative payment methods

Ecommerce in Europe is shaped by diversity. While cards remain dominant in some regions, APMs are taking a larger share of online payments each year.

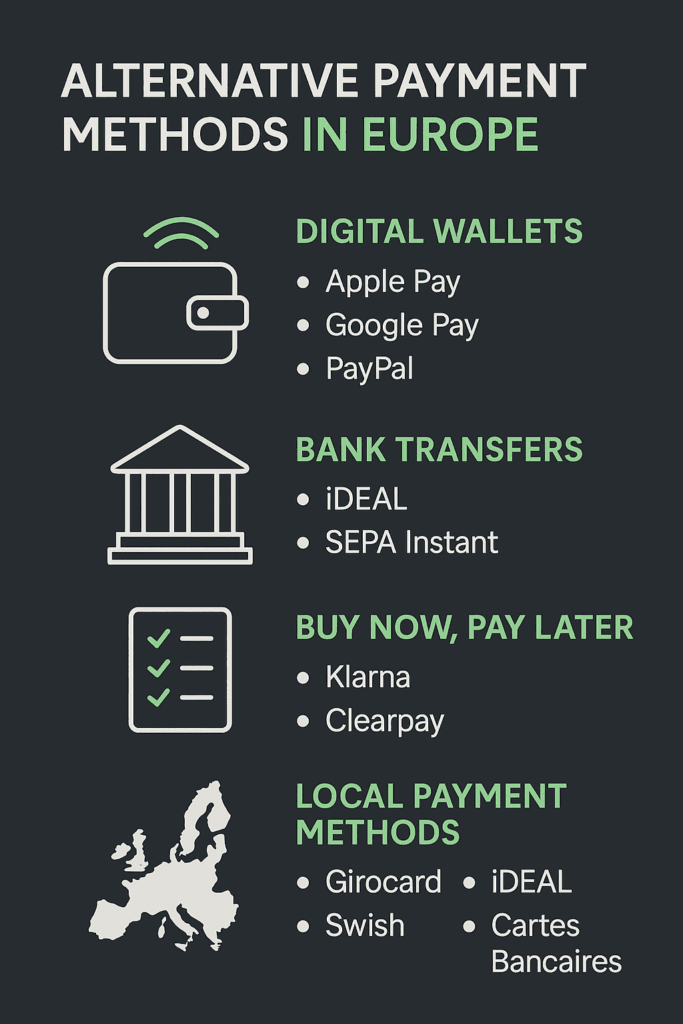
  • Wallets like PayPal, Apple Pay, and Google Pay are mainstream across most markets.
  • Bank-to-bank transfers are accelerating with SEPA Instant and open banking APIs.
  • National schemes continue to dominate local markets, such as iDEAL in the Netherlands and Girocard in Germany.

Data from 50 payment and merchant statistics shaping Europe in 2025 shows that more than 60% of online shoppers now expect multiple APMs at checkout. Merchants that support them see higher approval rates and lower cart abandonment.

Country-level breakdown of APMs

Germany

German consumers prefer direct debit and local cards. Girocard, often co-badged with debit schemes, remains widely used. PayPal also has significant adoption in ecommerce.

Netherlands

iDEAL dominates Dutch ecommerce. More than 70% of online transactions flow through this bank-based method. Merchants entering this market must support iDEAL to compete effectively.

Nordics

Sweden’s Swish and Denmark’s MobilePay are leading mobile-first methods. Both are integrated into daily life and used for recurring as well as one-off payments.

France

Cartes Bancaires remains the national card network, but PayLib and wallets are gaining ground. Merchants must often support both cards and wallet-based flows.

UK

The UK combines card-on-file payments with newer options like Faster Payments and wallets. Buy Now Pay Later services have also gained strong traction.

Our guide to top payment methods in Europe explores these local preferences in greater detail and shows why localization is critical.

Wallets and digital-first methods

Wallet adoption continues to grow across Europe. Apple Pay and Google Pay are built into mobile devices, making them easy for consumers to use. PayPal remains a trusted brand, especially in cross-border transactions. Buy Now Pay Later providers like Klarna are reshaping ecommerce for younger demographics.

The European Payments Initiative is also rolling out Wero, a digital wallet designed to compete with global providers and standardize payments across EU countries. For merchants, Wero signals the increasing importance of EU-backed solutions.

For a broader overview of how wallets are changing checkout behavior, see our report on digital wallets in Europe.

Bank-to-bank rails and open banking

Open banking APIs, combined with SEPA Instant, are creating account-to-account (A2A) payment flows that bypass cards entirely. These methods allow merchants to accept payments directly from customer accounts with lower fees and faster settlement.

The EU Instant Payments Regulation, which requires banks to support SEPA Instant, will further accelerate adoption. This will bring APMs closer to real-time status and reduce reliance on traditional card infrastructure.

More details are covered in our guide on real-time payments across Europe.

Compliance and security considerations

Adopting alternative payment methods requires merchants to meet strict compliance standards:

  • PSD2 and SCA: Strong Customer Authentication applies to most APMs, including wallets and open banking flows. Merchants must ensure exemptions are applied correctly to avoid declined payments.
  • GDPR: Wallets and account-to-account payments involve storing and processing sensitive data. Customers must have transparency and control over how their data is used.
  • AML and KYC: For bank-to-bank and direct debit payments, merchants must align with anti-money laundering rules. This is especially relevant for platforms that process payments on behalf of multiple sellers.
  • Refunds and disputes: National rules, such as SEPA Direct Debit’s refund framework, affect how disputes are handled and what liability merchants face.

For more detail on regulatory frameworks, see our guide to embedded payments compliance in Europe.

Why orchestration is key for APM integration

Supporting APMs across multiple European countries without orchestration is complex and costly. Each method has its own technical requirements, compliance checks, and reporting standards. Payment orchestration simplifies this through a single control layer:

  • Unified access: One integration unlocks multiple APMs, from iDEAL to Swish.
  • Dynamic routing: Merchants can prioritize local methods where they perform best.
  • Scalability: Adding new APMs does not require new one-off integrations.
  • Centralized compliance: Fraud checks, SCA flows, and reporting can be managed in one place.

For merchants expanding into multiple EU markets, orchestration provides the flexibility and resilience that a single PSP cannot. See our analysis on why payment orchestration matters for European merchants expanding cross-border for more.

Roadmap for merchants

Merchants looking to implement APMs effectively should:

  1. Research market preferences: Identify which APMs dominate in each target country. Top payment methods in Europe is a useful starting point.
  2. Prioritize compliance: Map how PSD2, GDPR, and AML apply to each payment flow.
  3. Adopt orchestration: Use a single layer to integrate, route, and monitor APMs across borders.
  4. Optimize checkout UX: Present local APMs clearly, ensuring they are trusted and familiar to customers.
  5. Monitor performance data: Track approval rates, dispute levels, and adoption to refine the mix of APMs offered.

FAQ

What are the most popular alternative payment methods in Europe?

iDEAL in the Netherlands, Girocard and PayPal in Germany, Swish and MobilePay in the Nordics, and wallets like Apple Pay and Google Pay across many markets.

Is iDEAL only for Dutch customers?

Yes, iDEAL is specific to the Netherlands, but it sets an example of how strong national APMs can dominate local ecommerce.

How do SEPA Instant and open banking affect APM adoption?

They accelerate account-to-account payments, offering faster and lower-cost alternatives to cards.

Are APMs more secure than cards?

They often offer equal or higher security due to real-time bank authentication and strong encryption. Compliance with PSD2 makes them robust.

Can orchestration handle multiple APMs at once?

Yes. Orchestration allows merchants to integrate and manage multiple APMs across countries through one unified platform.

Alternative payment methods are shaping the future of European ecommerce. Consumers increasingly expect to pay with wallets, bank transfers, or trusted local schemes, not just cards.

Merchants that adapt to these expectations improve conversion, strengthen customer trust, and expand more effectively across borders. Orchestration is the most efficient way to integrate and manage APMs at scale, while meeting compliance requirements and reducing operational complexity.

Contact Gr4vy to streamline alternative payment method integration and build a checkout strategy that fits every European market.

Recurring payments in Europe: compliance and conversion strategies

Recurring payments are now a foundation of European commerce. From subscription streaming and SaaS to mobility passes and meal kits, customers expect seamless billing experiences that run in the background. For merchants, recurring payments drive predictable revenue and stronger customer relationships.

But recurring payments in Europe come with challenges. Regulations like PSD2, GDPR, and SEPA Direct Debit rules demand strict compliance. At the same time, conversion is threatened by failed renewals, expired cards, and abandoned subscriptions. Merchants that balance compliance and conversion strategies will succeed in building sustainable subscription revenue.

The growth of recurring payments in Europe

The subscription economy continues to expand across European markets. Consumers are signing up for services in media, retail, and financial products at higher rates every year. SaaS adoption is surging among businesses, and recurring billing models are reshaping everything from transport passes to household essentials.

Recent data shows that recurring payments already account for a large share of card transactions and direct debit activity in major markets. Consumers in Germany lean heavily on direct debit for subscriptions, while UK customers often rely on recurring card charges. This diversity underscores the need for localization.

Our report on 50 payment and merchant statistics shaping Europe in 2025 shows that merchants offering multiple payment methods at checkout, including recurring-friendly options, consistently achieve higher conversion.

Compliance requirements for recurring payments

PSD2 and Strong Customer Authentication (SCA)

Under PSD2, Strong Customer Authentication is required for most online transactions. For recurring payments, the rules differ depending on the type:

  • Initial transaction: Requires SCA (e.g., biometric or two-factor authentication).
  • Subsequent transactions: Often exempt, provided they are for the same amount and paid to the same merchant.

This creates opportunities for smoother experiences but requires merchants to implement exemptions correctly. Failing to do so risks declined payments.

GDPR and data handling

Recurring payments require storing sensitive customer data, including payment credentials. GDPR mandates strict rules on how data is collected, stored, and processed. Merchants must ensure transparency, secure consent, and allow customers to control or withdraw data at any time.

SEPA Direct Debit rules

For eurozone countries, SEPA Direct Debit remains one of the most popular recurring payment methods. Merchants must follow strict mandates on pre-notification, authorization, and refund rights. Understanding these rules is vital for reducing disputes.

AML and KYC

Platforms that facilitate recurring payments between multiple sellers and buyers may need to perform anti-money laundering and know-your-customer checks. Compliance obligations expand as platforms grow.

For deeper insights into how these frameworks overlap, see our guide on embedded payments compliance in Europe.

Conversion challenges in recurring models

Recurring payments also introduce unique conversion challenges.

  • Card expirations: Many recurring charges fail because the customer’s card is expired. Without a strategy for updating card details, churn increases.
  • Insufficient funds: Recurring billing dates often coincide with customer cash-flow issues. Failed renewals create lost revenue.
  • SCA failures: If exemptions are not applied properly, customers may be asked to re-authenticate, leading to higher drop-off.
  • Regional differences: In Germany, recurring direct debit is trusted and expected. In the UK, recurring card charges are common. In Spain, mobile-first customers are looking for wallet-based recurring payments.

Our analysis of top payment methods in Europe shows that failing to adapt recurring methods to local preferences is one of the main drivers of subscription churn.

Strategies to improve compliance and conversion

Merchants can strengthen both compliance and conversion by implementing targeted practices:

  1. Smart retry logic: Use intelligent retry strategies when payments fail due to insufficient funds or temporary network issues. Spacing retries over different times of the day or billing cycles can recover revenue without frustrating customers.
  2. Dynamic routing across acquirers: Transactions should be routed to the acquirer with the best authorization rates for that region or card type. This not only improves conversion but also reduces costs. For a deeper view of how routing shapes merchant performance, see our analysis of acquirer fee optimization in Europe.
  3. Network tokenization: Tokenization helps merchants avoid failed transactions caused by expired cards. Tokens update automatically with new card details, ensuring continuity in subscription billing.
  4. Localized recurring methods: Each market has its own recurring payment expectations.
    • Germany favors SEPA Direct Debit.
    • The UK prefers card-on-file models.
    • Southern Europe shows higher adoption of wallet-based recurring charges.
      Offering localized methods reduces churn by aligning with consumer habits.
  5. Real-time payment rails: Emerging real-time systems like SEPA Instant open opportunities for recurring payments that settle immediately. Merchants should prepare for recurring use cases tied to instant settlement. More context can be found in our guide on real-time payments across Europe.

How orchestration supports recurring payments

Payment orchestration is central to managing recurring payments at scale:

  • Unified compliance: Orchestration platforms integrate SCA flows, GDPR-safe data storage, and PCI DSS vaulting in one layer.
  • Multi-method flexibility: Merchants can support SEPA Direct Debit, cards, wallets, and real-time options from a single integration.
  • Churn reduction: Orchestration enables retry logic and failover between PSPs, protecting revenue from technical or authorization failures.
  • Centralized reporting: Disputes, refunds, and regulatory audits become easier when data is consolidated.

This flexibility is why orchestration is better suited than a single PSP for recurring business models. For more, see our guide on payment orchestration vs PSP in Europe.

Roadmap for merchants

  1. Map compliance obligations across each market where recurring billing is active.
  2. Build localized checkout to support recurring-friendly payment methods in each country.
  3. Adopt orchestration to unify recurring billing operations across multiple PSPs.
  4. Implement retry and tokenization to reduce failures from expired cards or insufficient funds.
  5. Monitor conversion data continuously and adjust routing strategies to maximize approval rates.

For more on regional patterns and subscription preferences, see our report on European retail payment trends in 2025.

FAQ

What is SCA for recurring payments in Europe?

SCA is required for the first payment in a recurring series. Subsequent charges for the same amount and merchant are usually exempt.

Can recurring payments skip authentication under PSD2?

Yes, if exemptions are applied correctly. However, merchants must configure flows to ensure compliance or risk higher decline rates.

What is the role of SEPA Direct Debit?

It is a trusted and widely used recurring method in eurozone countries, especially Germany and the Netherlands.

How can merchants reduce recurring payment failures?

Using tokenization, retry logic, and multi-acquirer routing significantly reduces failed charges and customer churn.

Does orchestration support subscription billing?

Yes. Orchestration enables merchants to integrate recurring-friendly methods, automate retries, and manage compliance across markets.

Recurring payments are essential for subscription businesses in Europe. But without the right strategy, merchants risk high failure rates and compliance gaps. Customers expect seamless renewals, regulators demand strict controls, and competition is unforgiving.

Merchants that combine compliance with conversion strategies will protect revenue and build long-term customer relationships. Payment orchestration delivers the flexibility and resilience needed to achieve both.

Contact Gr4vy to streamline recurring payments, improve conversion, and stay compliant across European markets.

Fraud prevention in European e-commerce

E-commerce fraud continues to rise across Europe in 2025. Criminals are exploiting real-time payment rails, social engineering, and identity theft at greater scale. Authorized push payment scams are growing quickly, and deepfake impersonation is becoming harder to detect.

Merchants cannot rely on generic global tips. Europe has its own regulatory structures, from PSD2 to GDPR, and soon PSD3. The European Payments Council and the Euro Retail Payments Board have both flagged fraud as one of the region’s top challenges. Fraud prevention here requires approaches that address regional realities, shared data responsibilities, and orchestration across multiple providers.

This article examines the current fraud landscape in European e-commerce and offers strategies tailored for merchants operating in this region.

Fraud landscape in Europe today

Rising threat levels

Reports across 2024 and 2025 show fraud levels climbing. Social engineering scams account for a large share of losses. Investment scams and impersonation schemes have surged. Criminals are targeting merchants that support instant transfers, where settlement happens before checks can flag issues.

Authorized push payment fraud is now one of the fastest-growing categories. In the UK alone, more than £450 million in losses were reported in 2023. Across Europe, merchants are facing similar scams, where customers are tricked into sending money directly to fraudsters.

Collaboration on fraud data

The European Payments Council has introduced the Fraud Information and Data Sharing Task Force (FRIDA TF). This group works to enable data sharing across PSPs and banks. The goal is to create early warning systems that can stop fraud faster. For merchants, this signals a shift: fraud prevention is moving toward shared responsibility and real-time intelligence.

Regulatory push

The Euro Retail Payments Board has recommended EU-wide fraud data collaboration and new liability frameworks. Member states are strengthening national rules too. In Germany, BaFin is pressing platforms to improve real-time fraud checks. In France, the ACPR has placed stronger obligations on marketplaces. In the UK, merchants are facing liability shifts under the Economic Crime Act if they fail to implement reasonable fraud prevention.

Merchants expanding across Europe cannot ignore these changes. Fraud protection now ties directly to compliance.

Why generic fraud tips don’t work in Europe

Many global fraud prevention guides repeat the same advice: use rule-based filters, run manual reviews, and monitor transactions for anomalies. These practices are useful, but they are not enough in Europe.

European e-commerce operates under unique pressures:

  • Real-time rails like SEPA Instant require fraud checks within seconds. Delays are not an option.
  • Multi-country compliance adds complexity. GDPR governs data, PSD2 and soon PSD3 govern authentication, and AML rules vary across borders.
  • Shared liability is increasing. In some jurisdictions, merchants may be responsible if regulators decide fraud controls were insufficient.

A fraud prevention strategy in Europe must be multi-layered, real-time, and built on orchestration.

Key fraud types affecting European merchants

  1. Social engineering: Customers manipulated into making payments. Often linked to push-payment scams.
  2. Identity theft and account takeover: Criminals use stolen credentials to access customer accounts and complete purchases.
  3. Synthetic identities: Fraudsters create fake but plausible identities, often combining real and fabricated data.
  4. Bot-driven attacks: Automated attempts to test stolen cards or exploit checkout flows.
  5. Refund fraud: Customers falsely claim goods were not received or returned.
  6. Deepfake impersonation: Fraudsters use AI tools to mimic voices or identities, particularly in B2B payment requests.

Each of these requires defenses that go beyond static rules. Merchants must integrate AI-based detection, real-time monitoring, and cross-provider collaboration.

Toward high-impact, Europe-specific strategies

Fraud prevention for European e-commerce in 2025 is about adapting to these realities. Strategies must integrate regulatory requirements, leverage orchestration, and use advanced tools like machine learning.

The next part of this article will explore seven high-impact strategies for merchants, explain how orchestration supports fraud prevention, and provide a practical roadmap for building a European fraud defense framework.

High impact strategies suited to Europe

Fraud prevention in 2025 requires region-specific measures. These strategies reflect regulatory changes, consumer habits, and merchant realities:

  1. Real-time fraud checks with verification of payee: Instant payment adoption means fraud must be detected in seconds. Verification of payee ensures the account details match the intended recipient, reducing spoofing and liability. See our analysis of real-time payments across Europe for more on instant settlement and fraud risks.
  2. Cross-provider fraud intelligence: Fraud data sharing is becoming essential. Merchants can strengthen defenses by working with providers and orchestration platforms that support intelligence exchange. Broader trends are covered in European retail payment trends in 2025.
  3. AI and adaptive risk scoring: Fraud tactics evolve quickly. Machine learning and behavioral analytics help merchants spot anomalies without increasing false declines. When connected through orchestration, these tools scale across all providers.
  4. Enhanced risk policies for merchants: Regulators expect merchants to implement stronger internal controls. Fraud prevention is no longer limited to banks or PSPs. Platforms and marketplaces must embed compliance frameworks as explained in embedded payments compliance in Europe.
  5. Behavioral and device intelligence: Device fingerprinting and velocity checks help identify bot attacks, account takeovers, and organized fraud. Merchants operating across borders can use orchestration to apply consistent device rules across acquirers.
  6. Chargeback and friendly fraud defense: Disputes and refund abuse remain common. Orchestration enables merchants to track data across providers, making it easier to respond to chargebacks and reduce losses. For more on regional payment habits and dispute patterns, see top payment methods in Europe.

How orchestration strengthens fraud defenses

Payment orchestration provides a foundation to make these strategies effective:

  • Unified fraud stack: Centralizes fraud tools, rules, and monitoring in one control layer.
  • Adaptive routing: Routes higher-risk transactions through stricter fraud engines or preferred acquirers.
  • Analytics and reporting: Gives merchants visibility into fraud trends across all PSPs and markets.
  • Resilience: Keeps checkout operational even if fraud-related issues hit one PSP.

These capabilities highlight why orchestration is a stronger model than relying on one PSP. For more on this, see our guide on payment orchestration vs PSP in Europe.

Roadmap for merchants

A fraud strategy in Europe should follow these steps:

  • Assess risk country by country: Fraud patterns differ across markets. Data in our 50 payment and merchant statistics provides benchmarks.
  • Adopt orchestration: Use a control layer to unify fraud defenses across PSPs.
  • Layer protections: Combine AI, device intelligence, payee verification, and manual reviews.
  • Collaborate on data: Work with providers that support fraud intelligence exchange.
  • Embed governance: Train staff, document fraud frameworks, and include fraud metrics in compliance reviews.

FAQ

What types of fraud are growing fastest in Europe?

Social engineering, authorized push payment scams, account takeovers, and refund fraud are on the rise, especially where instant payments are active.

How does verification of payee reduce fraud?

It checks the account name against the IBAN to prevent misdirected transfers and scams in instant payment flows.

Are merchants liable for fraud prevention gaps?

Yes. Regulators are increasingly holding merchants accountable when internal fraud controls are weak, especially in embedded or marketplace payments.

How does AI improve fraud detection?

AI adapts to evolving patterns and reduces false positives, allowing merchants to block fraud without harming genuine customers.

Does orchestration help beyond cost savings?

Yes. Orchestration provides fraud resilience, centralizes compliance, and enables merchants to apply consistent defenses across markets.

Fraud in European e-commerce is evolving fast. Real-time payments, new scams, and shifting regulations require merchants to strengthen defenses. Generic fraud tips are not enough.

Merchants need layered protections, real-time verification, and orchestration to stay ahead. By centralizing fraud prevention across providers, orchestration makes compliance easier, improves resilience, and protects revenue.

Contact Gr4vy to develop a tailored fraud prevention strategy that aligns with the scale and complexity of European e-commerce.

Acquirer fee optimization in Europe: Strategies for faster authorization and lower costs

Payments drive revenue, but they also carry significant cost. For European merchants, acquirer fees are one of the largest ongoing expenses in payment acceptance. These fees cover processing, settlement, and network access, but they vary by market, transaction type, and provider.

Optimization is more than cost reduction. Lower acquirer fees combined with higher authorization rates directly improve conversion and margins. Merchants expanding across Europe cannot treat acquiring as a fixed expense. They must treat it as an area for continuous optimization.

Understanding acquirer fees

Acquirer fees are what merchants pay to their acquiring bank or PSP to process transactions. These fees typically include three main components:

  • Interchange fees: Paid to the cardholder’s bank. Regulated in the EU for consumer cards.
  • Scheme fees: Paid to card networks like Visa and Mastercard for using their infrastructure.
  • Acquirer markup: The margin the acquiring bank or PSP charges the merchant.

The total cost per transaction depends on card type (debit, credit, corporate), country, and whether the transaction is processed domestically or cross-border.

For merchants with high volumes, even small differences in acquirer fees add up to significant costs. Without visibility and control, many businesses overpay and suffer lower approval rates.

The European context

Europe is a unique payments region. The EU has capped interchange fees for consumer cards under the Interchange Fee Regulation (IFR) at 0.2% for debit and 0.3% for credit. This creates a level of predictability. But scheme fees and acquirer markups remain variable, and corporate and commercial cards are not capped.

Differences also emerge from:

  • Domestic vs cross-border acquiring: Domestic processing usually yields higher approval rates and lower costs. Cross-border acquiring often carries extra fees and lower authorizations.
  • Currency conversion: Non-eurozone markets like the UK, Sweden, or Denmark introduce FX costs.
  • Market preferences: In countries such as Germany, alternative methods like bank transfers reduce reliance on card acquiring. In the Netherlands, iDEAL dominates online transactions, limiting card volumes.

For merchants operating in multiple European countries, the acquiring strategy must adapt to each local context.

Many merchants focus only on reducing headline fees. But authorization rates play an equally critical role in the total cost of payments. A low authorization rate increases the effective cost per successful transaction.

Example:

  • If authorization rates are 95%, fees on 100 transactions apply to 95 approved.
  • If authorization rates drop to 85%, fees still apply to 100 attempts but only 85 succeed.

That gap increases the cost of each approved payment.

Authorization rates often improve with local acquiring. Processing transactions domestically reduces declines linked to fraud checks, cross-border mismatches, or issuer preferences. Dynamic routing and network tokenization also help reduce soft declines, further improving approval rates.

Merchants must consider both sides: lowering fees and raising approvals. This is where acquirer optimization becomes a strategic lever, not just a cost-saving exercise.

For more detail on the role of wallets and alternative methods in Europe’s authorization landscape, see our analysis of digital wallets in Europe.

Why optimization matters now

Three forces make acquirer fee optimization more urgent in Europe:

  1. Regulatory pressure: With interchange capped, acquirer markups and scheme fees are the main levers for cost management.
  2. Consumer habits: Wallets, instant payments, and local schemes are changing transaction flows, but cards remain central in many markets. Optimizing card acquiring is still crucial.
  3. Cross-border expansion: Merchants growing across the EU need multiple acquirer relationships. Without orchestration, this complexity is hard to manage.

Merchants that treat acquiring as static risk higher costs and lower conversion. Those that optimize achieve not only lower fees but also smoother checkout and higher approval rates.

Strategies for acquirer fee optimization

Merchants have several levers they can pull to optimize acquirer costs while improving authorization rates.

Multi-acquirer setup

Working with more than one acquirer allows merchants to compare costs and performance. Relying on a single acquirer means accepting their fee structure and approval rates with no benchmark. Multi-acquirer setups introduce competition and flexibility.

Smart transaction routing

Merchants can route each transaction to the acquirer offering the best chance of approval at the lowest cost. A transaction from a French cardholder may perform better with a domestic acquirer than a cross-border one. Dynamic routing ensures each payment follows the best path.

Local acquiring

Domestic acquiring often avoids cross-border fees and increases approval rates. Issuers are more likely to approve transactions that appear local. Merchants processing in multiple EU countries benefit from having local acquiring options to reduce declines and lower costs.

Tokenization and retry logic

Card tokenization ensures secure storage while enabling intelligent retries on soft declines. Instead of losing a transaction, merchants can reattempt it with a different acquirer. This lowers lost revenue and improves conversion.

Data-driven negotiation

The more data you have, the stronger your position in negotiations. Merchants who track transaction volumes, approval rates, and routing performance can approach acquirers with hard numbers to argue for lower fees.

For an overview of why flexibility and resilience matter in these strategies, see our guide on payment orchestration vs PSPs in Europe.

How payment orchestration supports optimization

Optimizing acquirer fees across Europe is complex without orchestration. Merchants would need multiple direct integrations, data pipelines, and manual routing. Payment orchestration centralizes and automates these functions.

  • Single integration: One connection to an orchestration layer provides access to multiple acquirers.
  • Real-time monitoring: Merchants see performance data by acquirer, geography, and transaction type.
  • Automated failover: Transactions route to a backup acquirer instantly during outages.
  • Centralized reporting: Unified dashboards make it easier to identify cost savings and negotiate fees.
  • Cross-border compliance: Orchestration supports PSD2, SCA, and local rules across markets, reducing compliance overhead.

Merchants can adapt quickly to market changes and regulatory shifts. This agility is critical in Europe, where regulation and consumer preference are evolving rapidly.

For context on how these shifts affect broader retail strategies, see our analysis of European retail payment trends in 2025.

Strategic guidance for European merchants

Merchants looking to optimize acquirer fees should:

  1. Benchmark performance: Measure current authorization rates, costs, and declines across markets.
  2. Adopt orchestration: Use a central layer to integrate multiple acquirers and monitor performance in real time.
  3. Invest in local acquiring: Where volumes justify it, local acquiring reduces fees and improves approval rates.
  4. Leverage data: Use transaction and routing data in negotiations to secure better acquirer terms.
  5. Balance cost and customer experience: Lower fees are valuable, but higher approval rates often deliver bigger returns through improved conversion.

FAQ

What drives acquirer fees in Europe?

They are made up of interchange fees, scheme fees, and acquirer markup. Interchange is regulated for consumer cards, but scheme fees and acquirer markup vary widely.

How do cross-border transactions affect costs?

Cross-border acquiring often carries extra scheme fees and lower authorization rates compared to domestic acquiring.

Does using multiple acquirers lower fees?

Yes. Multi-acquirer setups introduce competition, give merchants flexibility, and allow routing to the lowest-cost option.

How do acquirer fees impact authorization rates?

Higher fees alone don’t guarantee approvals. Local acquiring and smart routing improve success rates, reducing the effective cost per approved transaction.

What role does orchestration play in fee optimization?

Orchestration centralizes acquirer management, enables dynamic routing, provides failover protection, and consolidates reporting for smarter negotiations.

Acquirer fees represent one of the most important cost centers in European payments. Optimizing them is not only about lowering expenses. It is about improving authorization rates, raising conversion, and delivering a smoother customer experience.

Merchants that adopt orchestration gain the flexibility to work with multiple acquirers, route transactions intelligently, and negotiate from a position of strength. In Europe’s fragmented market, this approach is essential for scaling efficiently.

Contact Gr4vy to see how payment orchestration helps reduce acquirer costs and improve authorization rates across Europe.

Embedded payments compliance in Europe: What merchants need to know

Embedded payments are reshaping commerce in Europe. From marketplaces and ride-hailing platforms to SaaS products and retail apps, more businesses are building payment experiences directly into their workflows. Customers pay inside the app without being redirected. For merchants, this means higher conversion and tighter control of the customer journey.

But embedding payments also creates new responsibilities. Once a platform facilitates transactions between buyers and sellers, regulators may view it as taking on roles that go beyond standard merchant acceptance. This brings requirements tied to payment services, data handling, and customer verification. For merchants expanding in Europe, compliance is not optional. It is central to growth.

What are embedded payments?

Embedded payments integrate payment functionality directly into a non-financial product or service. Examples include:

  • A marketplace that enables customers to pay sellers within the platform.
  • A ride-hailing app that processes fares without redirecting to an external gateway.
  • A SaaS product that allows users to pay for subscriptions inside the platform.
  • Retail apps that support one-click checkout tied to stored cards or wallets.

The appeal is clear: seamless experience, reduced friction, and more control for the merchant. But with control comes regulatory exposure.

Core compliance requirements in Europe

Merchants offering embedded payments must consider multiple layers of European compliance.

PSD2 and Strong Customer Authentication (SCA)

The revised Payment Services Directive requires strong authentication for online payments. Platforms embedding payments must ensure transactions meet SCA standards. This often means integrating biometric or two-factor authentication through their PSPs.

PCI DSS

Handling card data requires compliance with the Payment Card Industry Data Security Standard. Merchants embedding payments need to ensure cardholder data is stored, processed, and transmitted securely. Tokenization and vaulting reduce exposure, but responsibility remains.

AML and KYC

When platforms facilitate payments between third parties, regulators may require them to perform anti-money laundering checks and know-your-customer verification. This is especially relevant for marketplaces and gig platforms where multiple sellers operate under one umbrella.

GDPR and data privacy

Payment data is personal data. Platforms embedding payments must follow GDPR rules on collection, storage, and cross-border transfers. Customers must have visibility and control over their data.

National regulators

Beyond EU-level rules, countries have their own oversight. Germany’s BaFin, France’s ACPR, and the UK’s FCA all supervise payment activity. A platform expanding across borders may need to comply with each.

Risks of non-compliance

Failure to meet compliance standards has consequences:

  • Regulatory fines can reach millions of euros under GDPR and PSD2 violations.
  • Loss of license or access to payment services can halt business operations.
  • Reputational damage undermines customer trust.
  • Operational costs rise when remediation is needed after an audit or investigation.

Embedded payments open doors to new revenue, but without a compliance framework they expose merchants to risks that can outweigh the benefits.

How embedded payments intersect with regulation

Embedded payments blur the line between merchants and financial institutions. Platforms that only used to list products or connect users are now also handling funds. Regulators treat this differently.

Marketplaces, SaaS platforms, and gig-economy apps may fall under payment services rules when they facilitate transfers between buyers and sellers. This means they must either:

  • Obtain their own payment license, or
  • Partner with licensed PSPs or orchestration platforms that cover regulatory requirements.

The shared-responsibility model is becoming common. Licensed partners hold compliance responsibility for settlement, fraud prevention, and reporting. Merchants remain responsible for the customer experience and ensuring their providers align with PSD2, AML, and GDPR.

Why orchestration helps with compliance

Payment orchestration adds a structured layer that reduces compliance risk for embedded payments.

  • Centralized control: Merchants manage payment data, routing, and reporting in one place. This simplifies audits.
  • PCI DSS readiness: Orchestration platforms provide tokenization and secure vaulting to reduce exposure to sensitive data.
  • Multi-PSP strategy: Orchestration connects to multiple PSPs, ensuring compliance coverage in each market without multiple direct contracts.
  • Dynamic routing: Transactions can be sent through providers that meet specific compliance or regulatory requirements in different jurisdictions.
  • Resilience: Failover to backup providers reduces downtime, keeping services available during audits or provider issues.

For context on why orchestration is a stronger model for European growth, see our guide on payment orchestration vs PSPs in Europe.

Strategic guidance for merchants

Merchants planning to embed payments across Europe should take a structured approach:

  1. Map regulatory exposure: Identify where your business model makes you responsible for PSD2, AML, or local financial rules.
  2. Partner strategically: Use PSPs and orchestration platforms that already hold licenses and meet local requirements.
  3. Prioritize data protection: Align embedded payment systems with GDPR and PCI DSS from the start.
  4. Plan for scale: Compliance requirements expand as you enter new markets. Build flexibility into your payment stack now.
  5. Monitor regulation: New rules such as the EU Instant Payments Regulation will change settlement norms. Merchants must stay ahead.

For more detail on how consumer adoption and compliance go hand in hand, see our report on European retail payment trends in 2025.

FAQ

What compliance rules apply to embedded payments in Europe?

PSD2, GDPR, AML directives, and PCI DSS apply, along with local supervision by regulators such as BaFin, ACPR, and the FCA.

Do platforms need a financial license?

Sometimes. Marketplaces and apps that handle funds between third parties may need a license or must work with licensed PSPs.

How does orchestration reduce compliance complexity?

It centralizes tokenization, reporting, and routing. This reduces the merchant’s exposure to sensitive data and simplifies audits.

What is the role of KYC in embedded payments?

KYC is critical when onboarding sellers, drivers, or freelancers in platforms. Regulators require checks to prevent fraud and money laundering.

How do GDPR and PCI DSS overlap in embedded payments?

Both deal with data security. GDPR covers all personal data, while PCI DSS focuses on cardholder data. Together, they require strict controls on storage and access.

Embedded payments are transforming commerce in Europe. They create frictionless experiences for customers and new revenue streams for merchants. But they also come with regulatory obligations that cannot be ignored.

Merchants expanding in Europe must address PSD2, GDPR, PCI DSS, and AML requirements while adapting to national rules. Without a strategy, compliance risks can outweigh growth opportunities.

Payment orchestration provides the structure to manage these challenges. It simplifies compliance, centralizes data, and reduces reliance on any single provider. For merchants embedding payments into their platforms, orchestration is not an add-on — it is the foundation for compliance and growth.

Contact Gr4vy to prepare your embedded payments strategy for European compliance.

Why payment orchestration matters for European merchants expanding cross-border

Expanding across Europe is not a matter of flipping a switch. Each country has its own payment habits, regulations, and infrastructure. For merchants, this creates a patchwork of requirements that directly affect checkout performance.

A strategy that works in Germany may underperform in France. A wallet that converts in Spain may be irrelevant in the Netherlands. Add to this the constant updates to EU regulation, and the risk of service interruptions from a single provider, and the challenge of cross-border growth becomes clear.

Payment orchestration addresses these challenges. By providing a single layer that connects to multiple PSPs, acquirers, and payment methods, it gives merchants flexibility, resilience, and speed to market.

The complexity of cross-border payments in Europe

Europe is often seen as a single market, but payments show how fragmented it remains.

  • Regulations: PSD2, Strong Customer Authentication (SCA), and GDPR apply across the EU, but local regulators interpret them differently. Merchants must adjust to these nuances.
  • Currencies: While the euro dominates, the UK, Sweden, Denmark, and others operate outside the eurozone, requiring currency support and local settlement.
  • Consumer behavior: Preferences vary by country. In Germany, many consumers still rely on bank transfers and invoice payments. In France, Cartes Bancaires dominates. In Spain, Bizum is now part of daily life.

This mix of legal, technical, and consumer challenges forces merchants to manage multiple integrations, each with its own costs and risks. Without the right setup, expansion can slow or fail.

For a closer look at country-specific behaviors, see our analysis of European retail payment trends in 2025

Local preferences that shape success

Merchants expanding across borders must adapt checkout to local habits. Some examples:

  • Germany: Girocard and invoice-based payments remain strong. Many customers expect to pay after delivery.
  • France: Cartes Bancaires is the leading card scheme. Paylib adds wallet functionality for local use.
  • Spain: Bizum, integrated with most banks, is used by over 27 million people. PayPal also has a strong foothold.
  • Netherlands: iDEAL controls more than 70% of online transactions.
  • Nordics: Swish in Sweden and MobilePay in Denmark are widely used for P2P and retail payments.

Offering only cards or a single global wallet is not enough. Merchants that do not support local methods risk losing sales, even if their product or pricing is competitive.

You can read more about how wallets are reshaping checkout in our guide on digital wallets in Europe.

The limits of a single PSP

Payment Service Providers (PSPs) play a key role in merchant acceptance. They process transactions, manage acquiring, and provide fraud tools. But relying on one PSP for multi-market expansion creates limits.

  • Coverage gaps: No single PSP supports every local scheme. Merchants often face gaps when entering new markets.
  • Service risk: If the PSP suffers downtime, all transactions stop. For cross-border merchants, the impact can be severe.
  • Compliance challenges: Local regulatory differences are not always addressed by a global PSP. Merchants remain responsible for ensuring compliance.
  • Cost: Fees are often standardized, leaving merchants with little room to optimize transaction costs through routing.

For merchants serious about cross-border growth, relying on a single PSP is risky.

See our analysis on payment orchestration vs PSPs for a detailed breakdown of why this matters.

How payment orchestration supports expansion

Payment orchestration solves the limitations of a single PSP by acting as a control layer. Instead of being tied to one provider, merchants connect once to an orchestration platform and gain access to multiple PSPs, acquirers, and payment methods.

Core benefits include:

  • Multi-PSP connectivity: Add local schemes in each country without building new integrations.
  • Dynamic routing: Send transactions to the provider with the highest approval rate or lowest fee.
  • Failover protection: If one PSP goes down, traffic routes to another automatically.
  • Simplified compliance: Orchestration centralizes reporting and helps align with PSD2, GDPR, and local regulations.
  • Speed to market: Merchants launch in new countries faster because they don’t need to build from scratch.

This approach is particularly valuable in Europe, where market fragmentation creates complexity at every step.

Cross-border commerce in Europe: the scale of the challenge

European e-commerce is a €700 billion+ market in 2025. Growth is driven by merchants reaching beyond their home markets. Yet success depends on supporting local expectations.

  • In Spain, more than half of online shoppers use Bizum when offered.
  • In the Netherlands, iDEAL accounts for more than 70% of online transactions.
  • In Germany, invoice payments remain popular, while digital wallets are gaining traction.
  • In France, Cartes Bancaires still dominates card payments.

Consumers choose familiar methods. Merchants that fail to localize risk higher abandonment rates, even with competitive pricing or fast shipping.

Payment orchestration makes localization easier. Instead of separate projects for each country, merchants add new methods through one integration. This reduces time to market and limits technical debt.

For a broader look at these habits, see our analysis of European retail payment trends in 2025.

Orchestration in action: scenarios for merchants

Scenario 1: Entering Spain

A UK-based merchant expands into Spain. Customers expect Bizum. The merchant’s current PSP does not support it. Without orchestration, they would need a new PSP contract and custom integration. With orchestration, they add Bizum through the same platform, routing Spanish traffic locally while keeping UK transactions with their main PSP.

Scenario 2: Reducing downtime risk

A fashion retailer relies on one PSP across five European markets. When the PSP suffers an outage, thousands of transactions fail. Orchestration fixes this by routing traffic to a backup PSP automatically, protecting sales and customer trust.

Scenario 3: Optimizing costs

A subscription service processes high volumes across the EU. Fees vary by PSP and region. Orchestration enables dynamic routing, sending transactions to the cheapest provider or one with better approval rates. Savings at scale become significant.

Compliance and regulation

European regulation adds another layer of complexity:

  • PSD2 and SCA: Authentication is mandatory, but implementation differs by country.
  • GDPR: Data handling and storage must align with strict privacy rules.
  • Instant Payments Regulation: From 2025, euro-area PSPs must support instant transfers, and fees cannot exceed standard transfers.

Orchestration helps merchants align with these requirements. Reporting is unified, tokenization is centralized, and updates can be managed through one layer. This reduces the risk of non-compliance and fines.

Why orchestration is the cross-border model

Cross-border expansion is not only about payment acceptance. It is about resilience, cost efficiency, and speed.

  • Flexibility: Add and remove payment providers without new builds.
  • Resilience: Route traffic during outages.
  • Efficiency: Optimize routing for lower costs and better approval rates.
  • Speed: Launch in new markets quickly with pre-built connectors.

Merchants using orchestration adapt faster to consumer habits, regulatory shifts, and provider performance changes. 

FAQ

What is payment orchestration in Europe?

It is a control layer that connects merchants to multiple PSPs, acquirers, and payment methods through one integration.

Why is orchestration better than a single PSP?

A single PSP limits coverage, increases downtime risk, and reduces flexibility. Orchestration removes these barriers by supporting multiple connections at once.

How does orchestration reduce risk for cross-border merchants?

It ensures continuity during PSP outages and centralizes compliance, reducing exposure to regulation gaps.

Does orchestration support both cards and wallets?

Yes. Orchestration platforms integrate cards, wallets, bank transfers, and real-time rails in one checkout.

How does orchestration help with PSD2 and GDPR compliance?

It provides unified reporting, tokenization, and data management that align with EU requirements, simplifying audits and reducing compliance costs.

Cross-border expansion in Europe is full of promise but also full of complexity. Consumers expect local payment methods. Regulators demand strict compliance. PSP outages and costs threaten performance.

Payment orchestration addresses these challenges head-on. It delivers flexibility, resilience, and speed to market. Merchants serious about European growth need orchestration to scale successfully.

Contact Gr4vy to build a checkout strategy that supports your expansion across Europe.

What is sovereign cloud? An updated guide

Sovereign cloud has become a necessary step for industries under pressure to protect data, meet national regulations, and secure critical systems. With cloud adoption expanding quickly in Europe and other regions, companies face a clear challenge: complying with local laws while operating on global infrastructure. Sovereign cloud provides a way to reconcile the two.

This article breaks down what sovereign cloud means, why it matters, and how your business should approach it in 2025.

What is sovereign cloud?

Sovereign cloud refers to a cloud environment that meets national or regional requirements for data protection, privacy, and control. It allows organizations to store and process data within defined legal boundaries.

Key characteristics include:

  • Data residency in a specific country or region
  • Local control over infrastructure and operations
  • Protection from foreign access under laws like the US CLOUD Act
  • Independent encryption key management

Unlike traditional public cloud models, a sovereign cloud ensures that the hosting provider, operations, and legal jurisdiction all align with local rules.

Why data sovereignty matters

Data sovereignty is the principle that data is subject to the laws of the country where it is stored. In practice, this means that if your company stores customer or transaction data in a foreign country, it could be accessed by that country’s authorities under its laws.

This is a growing concern for:

  • European businesses subject to GDPR
  • Companies impacted by Schrems II and the invalidation of the Privacy Shield
  • Governments requiring full control over critical infrastructure

Fines for non-compliance with data regulations are significant. The GDPR allows penalties of up to 4% of annual global turnover. Businesses also face reputational damage when customers find out their data is accessible across borders.

Local regulators are paying attention. So are customers. Fines for non-compliance with data regulations are significant. The GDPR allows penalties of up to 4% of annual global turnover. Businesses also face reputational damage when customers find out their data is accessible across borders.

Data localization in payments is becoming more than a best practice. For many regions, it’s now a legal necessity.

Sovereign cloud vs. public cloud

Public cloud services are fast, scalable, and cost-effective. But they are often global by design. Data may be distributed across regions, and encryption keys may be managed by the provider.

Sovereign cloud, in contrast, ensures:

  • Infrastructure is located and operated locally
  • Legal jurisdiction stays within national borders
  • Data access is controlled by the customer or a trusted local entity

This model suits businesses in sectors like:

  • Government and public sector
  • Healthcare and life sciences
  • Banking and financial services
  • Retail platforms managing sensitive payment data

With sovereign cloud, the goal is simple. You stay in control of your data. You meet compliance rules without compromise.

Who benefits from sovereign cloud?

Not every company needs a sovereign cloud. But for some, it is a requirement. Here’s who should pay close attention:

Public institutions

Governments need to ensure national security. Sovereign cloud supports this by keeping sensitive workloads local.

Financial services

Banks, insurers, and payment providers operate under strict regulation. Sovereign cloud helps meet local reporting, auditing, and storage obligations.

Healthcare providers

Patient data must be stored and processed securely, often within national borders. Sovereign cloud supports compliance with health-specific regulations.

Multinational corporations

Companies operating in several regions face complex compliance challenges. Sovereign cloud lets them localize data operations without separate systems.

How cloud providers are responding

The major cloud players are building sovereign solutions. They offer configurations and partnerships that meet local control requirements.

Google

Through its Sovereign Cloud initiative, Google partners with local providers to offer services that meet national control and compliance needs.

Microsoft

Microsoft Cloud for Sovereignty is designed for public sector organizations, providing configurable compliance tools and data residency controls.

AWS

AWS offers Dedicated Local Zones and regional infrastructure that supports sovereignty goals, including customer-managed encryption keys.

Across the board, the strategy is similar:

  • Provide local infrastructure
  • Allow customer control over encryption
  • Limit foreign legal access to data
  • Work with local operators where needed

But these offerings vary in scope and governance. Businesses must evaluate them carefully.

What to consider before adopting a sovereign cloud

Moving to sovereign infrastructure is not simple. It involves trade-offs in cost, flexibility, and time to market.

Key questions to ask:

  • Where is my customer and transaction data stored today?
  • Do I control the encryption keys?
  • Which laws apply to my cloud provider’s operations?
  • Can I guarantee compliance with GDPR, Schrems II, or national security rules?
  • Will sovereign infrastructure slow down my product development?
  • Do I have the internal expertise to manage compliance at scale?

You should also review vendor lock-in risks. Some sovereign solutions tie you to a specific provider or ecosystem.

The case for cloud-native, sovereign-ready platforms

Not every business needs to move everything to a sovereign cloud today. But your infrastructure should be ready to adapt if required.

This is where cloud-native, infrastructure-as-a-service platforms offer an advantage. These platforms support flexible deployment across multiple environments.

A sovereign-ready architecture should support:

  • Local or regional data centers
  • Bring-your-own-key (BYOK) encryption
  • Support for multiple cloud providers or hybrid setups
  • API-first architecture for rapid integration

Payment platforms, in particular, benefit from this model. Payment data is highly regulated. Approval flows may span borders. A sovereign-ready platform gives you control without slowing you down.

Sovereignty and payments: an evolving requirement

Payment data is deeply tied to trust. Consumers expect security. Regulators expect compliance. Platforms need speed and flexibility.

The trend toward data localization is not slowing down. Countries like France, Germany, and Saudi Arabia are enforcing stricter rules. The EU continues to refine its stance on cross-border data flows. Sovereign readiness is now part of a responsible infrastructure strategy. Sovereign readiness is now part of a responsible infrastructure strategy.

Learn how orchestration enables global payment strategies without multiple integrations, while still complying with local requirements.

FAQ

What is the difference between public cloud and sovereign cloud?

Public cloud stores and processes data across global infrastructure. Sovereign cloud ensures that data remains within national borders, under local legal control, and often with customer-managed encryption keys.

Why is data sovereignty important for businesses?

It helps meet legal and regulatory requirements like GDPR or sector-specific rules in finance and healthcare. It also builds customer trust by ensuring sensitive data is protected from foreign access.

Who needs sovereign cloud?

Sovereign cloud is essential for governments, healthcare providers, financial services, and any business that handles regulated or sensitive data in strict jurisdictions.

Can sovereign cloud support scalability and innovation?

Yes. Many providers now offer sovereign solutions that retain the benefits of cloud—such as scale and availability—while complying with local data laws.

How does payment orchestration relate to sovereign cloud?

Payment orchestration platforms like Gr4vy support sovereign-ready infrastructure. They offer region-specific hosting, bring-your-own-key encryption, and control over how and where payment data is processed.

Gr4vy’s infrastructure-as-a-service model is built for this shift. We offer cloud-native payment orchestration with flexible deployment options, including regional data hosting and BYOK support. Because each merchant operates on their own single-tenant instance of Gr4vy, we make it easier to meet complex compliance and data residency requirements like GDPR, PCI-DSS, and other local regulations across the globe. This architecture removes the regulatory burden from merchants, giving them peace of mind and allowing them to scale faster and more securely. Whether expanding into Europe, the U.S., LATAM, or APAC, Gr4vy ensures your payments remain optimized, compliant, and reliable—no matter where you do business.

Contact Gr4vy to learn how to make your payments infrastructure sovereign-ready.